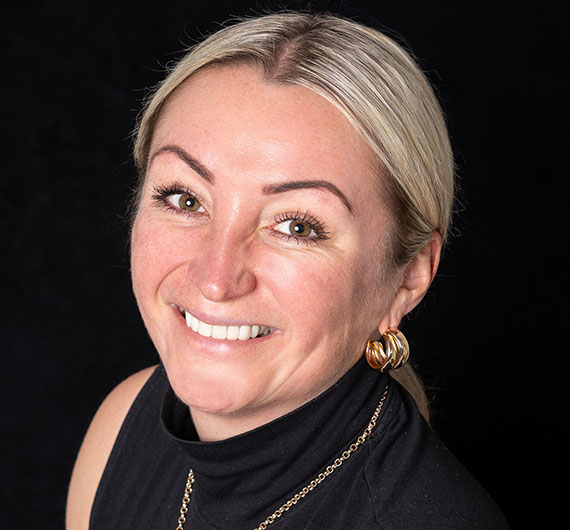
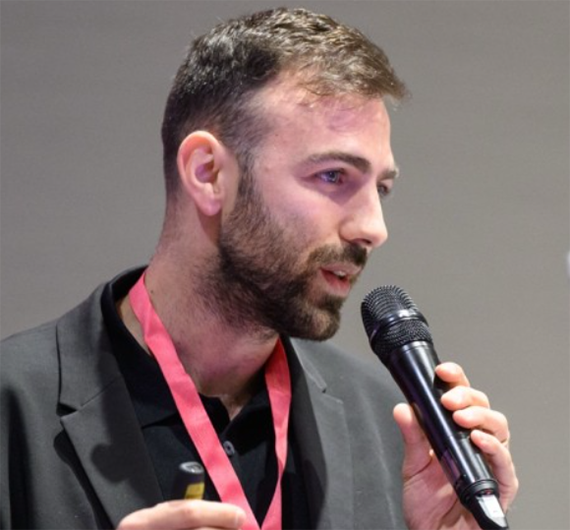
Lone Forland – Product designer and training manager, NorthGRC
Jakob Holm Hansen – CPO and co-owner, NorthGRC
Last year, the NorthGRC Platform went dark for 16 minutes. We're ISO 27001 certified. We build compliance software for a living. For those 16 minutes, none of that mattered.
This talk is about the gap that outage exposed — the distance between the compliance you've documented and the security you actually have on any given day. A certificate proves you wrote it down once. It doesn't prove it's still true this morning.
Join NorthGRC's Jakob and Lone for a straight, slightly uncomfortable account of what went wrong, why being the experts didn't save us, and what we started changing afterwards. Along the way: why static documentation can't keep pace with a threat landscape that now moves at machine speed, why NIS2, DORA, and NSM raise the stakes, and what you should demand from modern GRC platforms — including from vendors like us.
Lone Forland is an accomplished compliance and product expert with extensive experience in governance, risk management, and data protection. As Product Designer and Training Manager at NorthGRC, she has been instrumental in helping organisations navigate complex compliance requirements and get the most out of their GRC tools since 2007. Lone leads customer training, webinars, and educational content on information security, GDPR, and risk management best practices, empowering professionals to implement effective compliance programmes and maintain robust security standards. With a passion for making compliance accessible and practical, she regularly shares insights and guidance through blogs, courses, and live sessions.
Jakob Holm Hansen is the CPO and co-owner of NorthGRC and has extensive experience within information security and Governance, Risk, and Compliance (GRC). He has been part of the company since 2008, supporting organisations across sectors in strengthening their information security and compliance programmes. Jakob plays a central role in designing the NorthGRC platform and driving its ongoing development to support end-to-end GRC processes. Drawing on deep practical expertise and hands-on experience from a wide range of customers, he shares insights focused on turning complex security and compliance requirements into practical, value-creating solutions.